F5 401 CSE · SecurityCertified since 2012LTM · ASM · APM · AFM · DNS · XC
Learn F5 and be confident in production.
Certification training built from real production work. Every BIG-IP TMOS exam today, F5 Distributed Cloud (XC) from early 2027. Real labs, real traffic, and a clear path from passing the exam to running F5 with confidence.
Available on desktop, iOS and Android · No card needed for the free course
Get free lifetime access
Pass your F5 exam within 90 days, or get a full refund.
Complete the course, sit the exam twice within 90 days, and if you fail both times I refund you in full. See the terms
Why I can promise this: every course follows the official blueprint line by line, every lesson is shown on a live BIG-IP, and when you get stuck you ask me directly.
14 years F5-certified
Hands-on in production the whole time
5 TMOS modules
LTM, DNS, ASM, APM, AFM, all blueprint-mapped
Developer since 1995
30 years of application development behind the teaching
OWASP member
Six years in. Attacks taught from the attacker's side
From my students
Engineers who sat the exam and passed.
“
Graham took me through the 201, then the 301a and 301b. He teaches on a real BIG-IP and explains why things work, not just what to click. I passed all three in seven months.
Nikos [surname]
[Job title], [Company] · Passed all 3 in 7 months
Real labs
Eight BIG-IPs. Every GUI walkthrough you'll ever need.
Every course is taught on a lab of eight TMOS instances: a network layer, an application layer, external DNS and an internal SSO layer, the way a real estate is built. Concepts come as animated slides, then every configuration is walked through in the live BIG-IP GUI, step by step, so you see the policy learn, the signature fire and the request get blocked before you do it yourself. Lifetime access to every walkthrough.
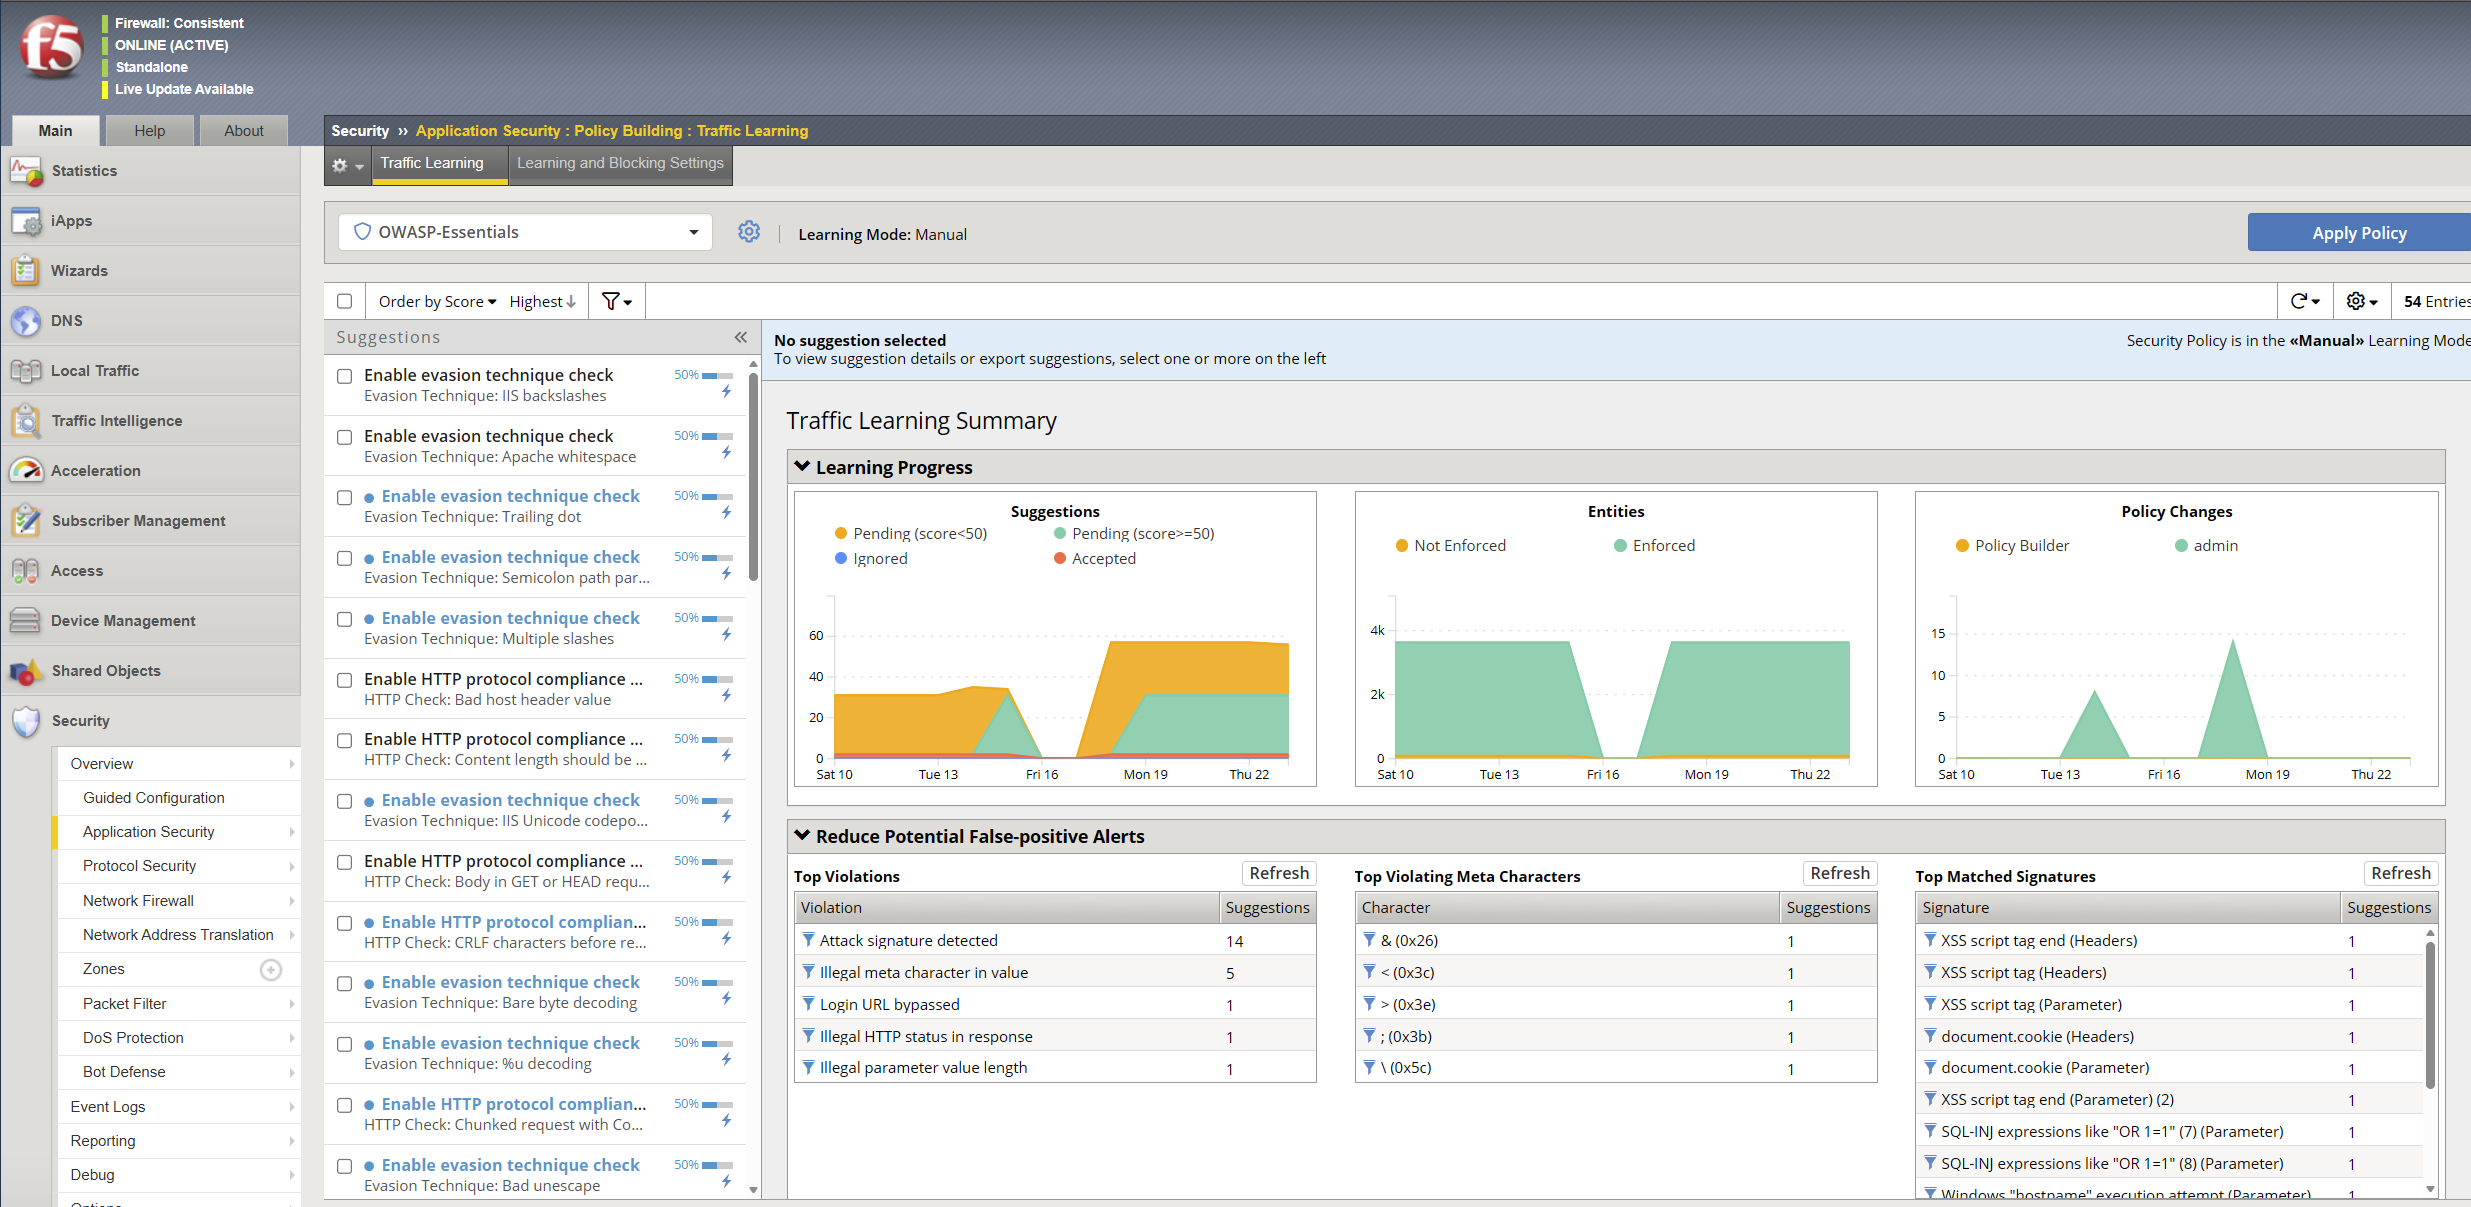
Policy learning in action
Traffic Learning on a real policy: suggestions scored, entities moving from staging to enforcement, false positives hunted down.
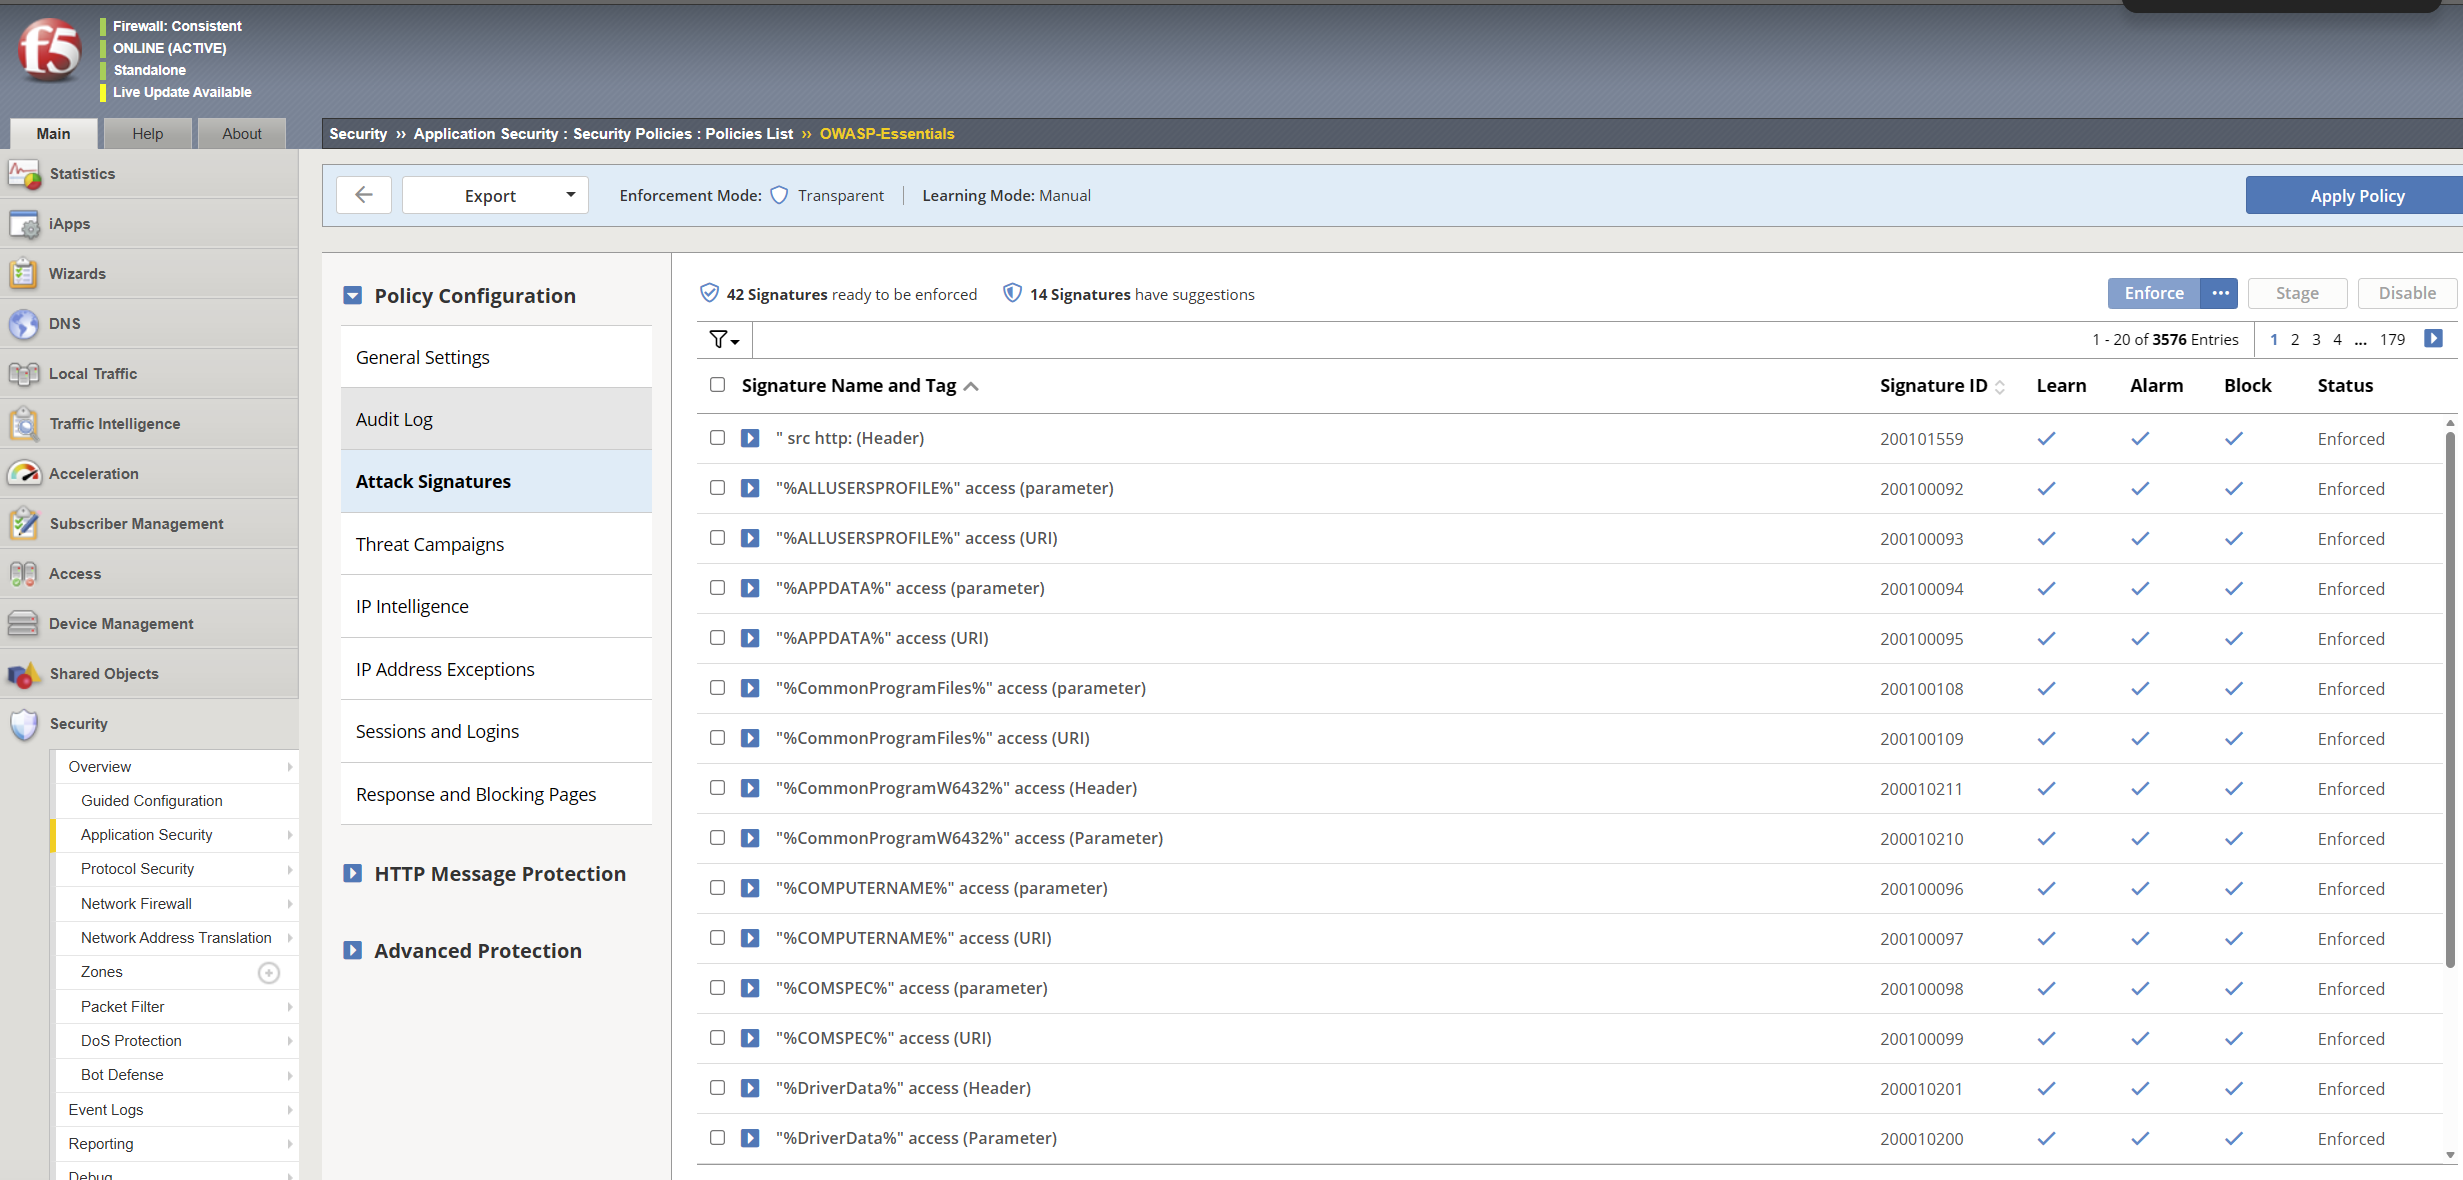
3,500 signatures, explained
Attack signatures in staging and enforcement, what Learn, Alarm and Block actually do, and when to flip them.
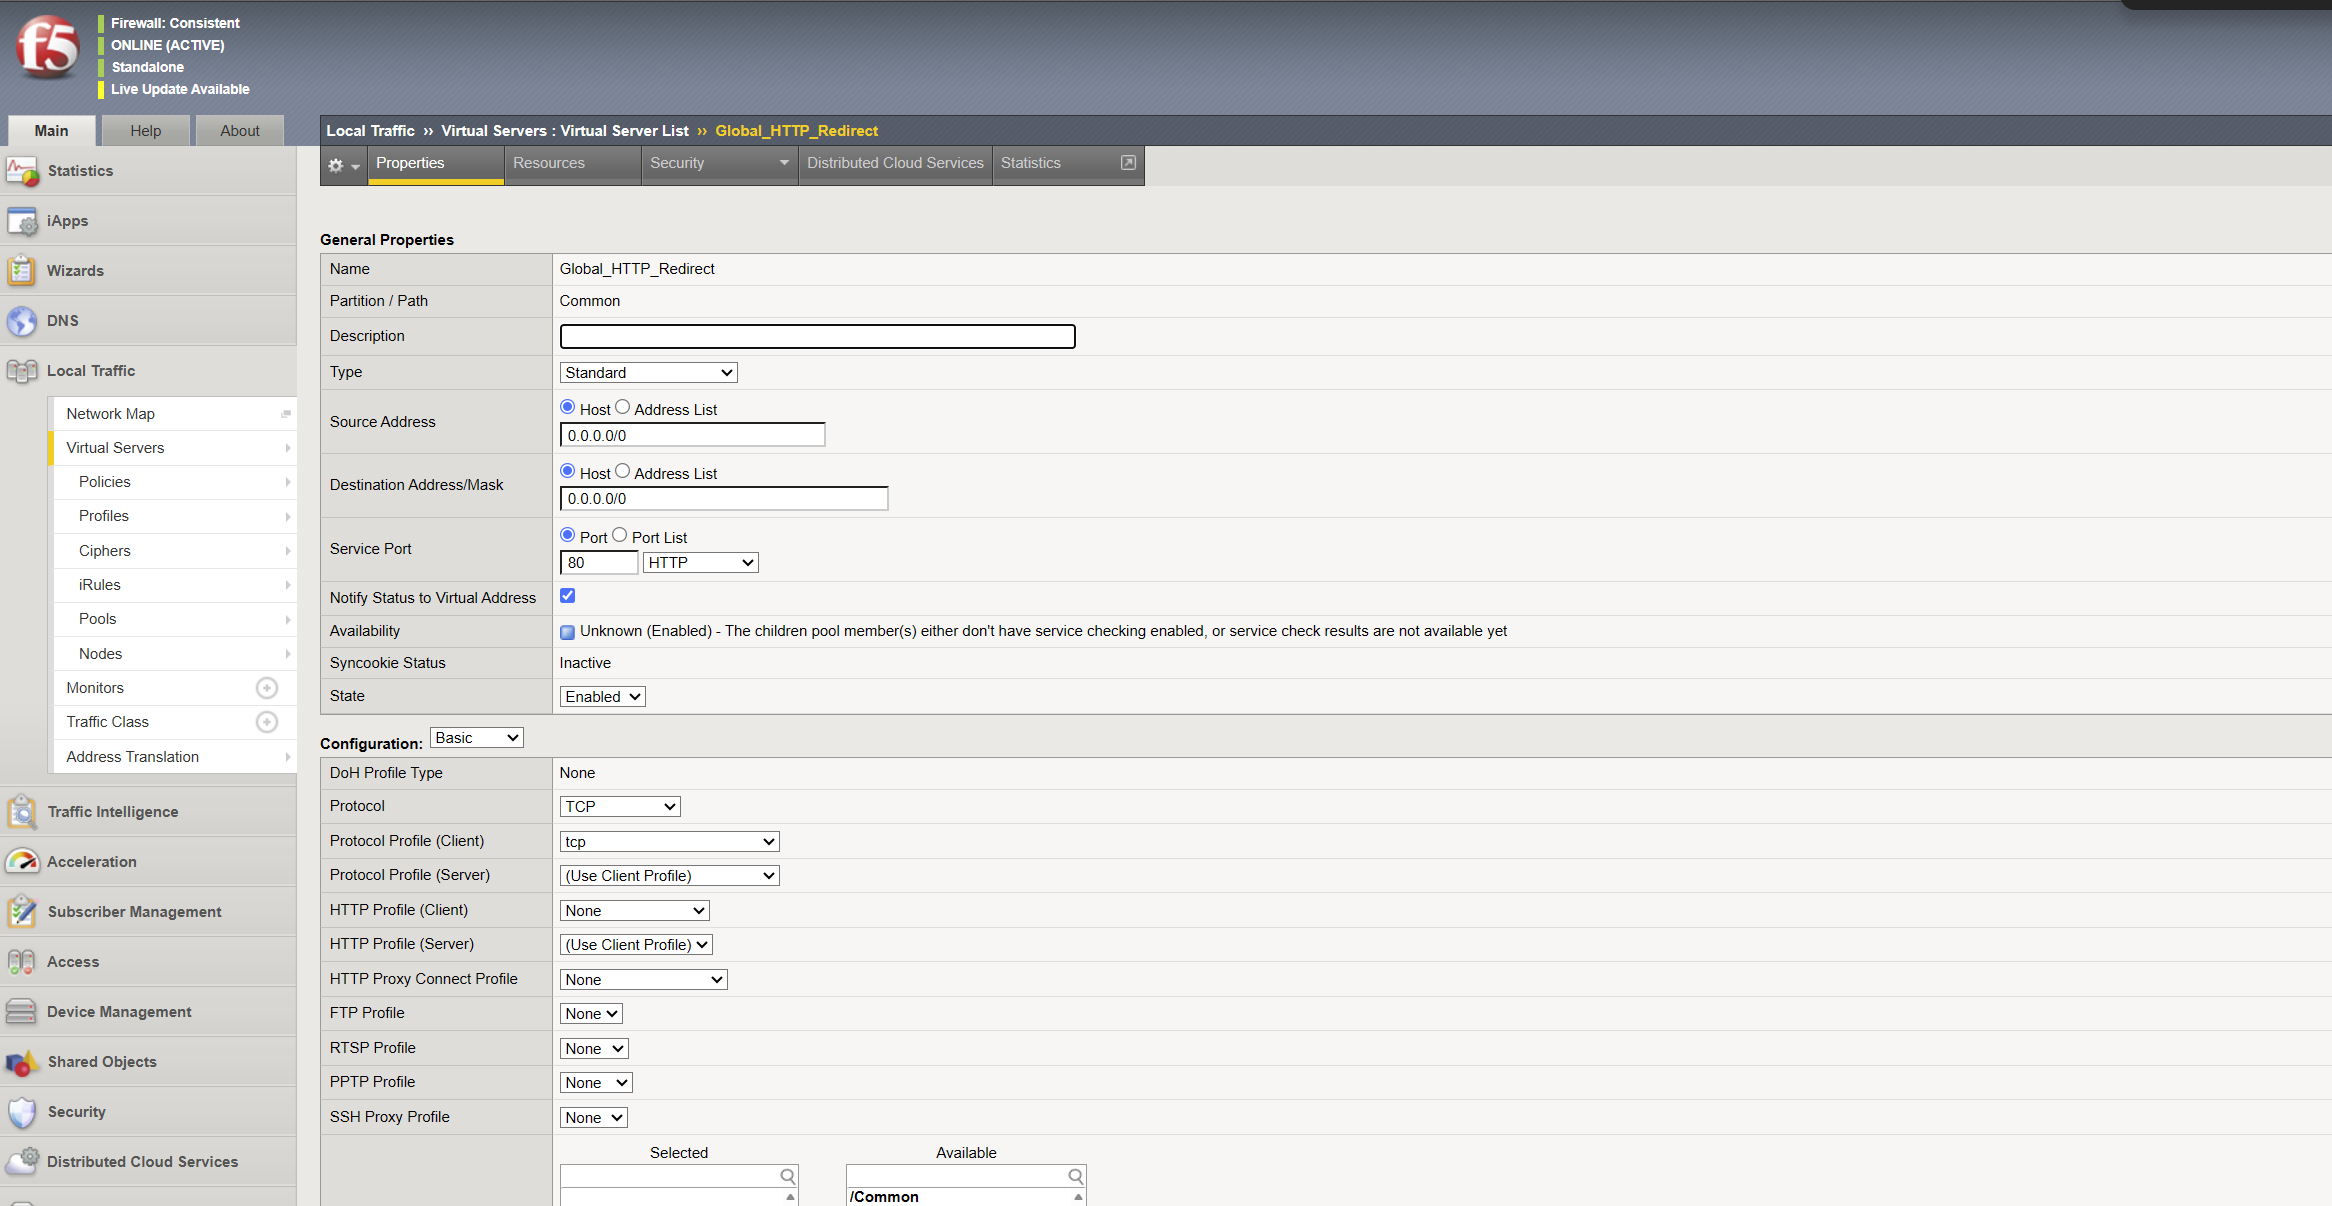
Virtual servers, the production way
Profiles, pools, security policies and logging wired up on a live virtual server, in the GUI and in TMSH.
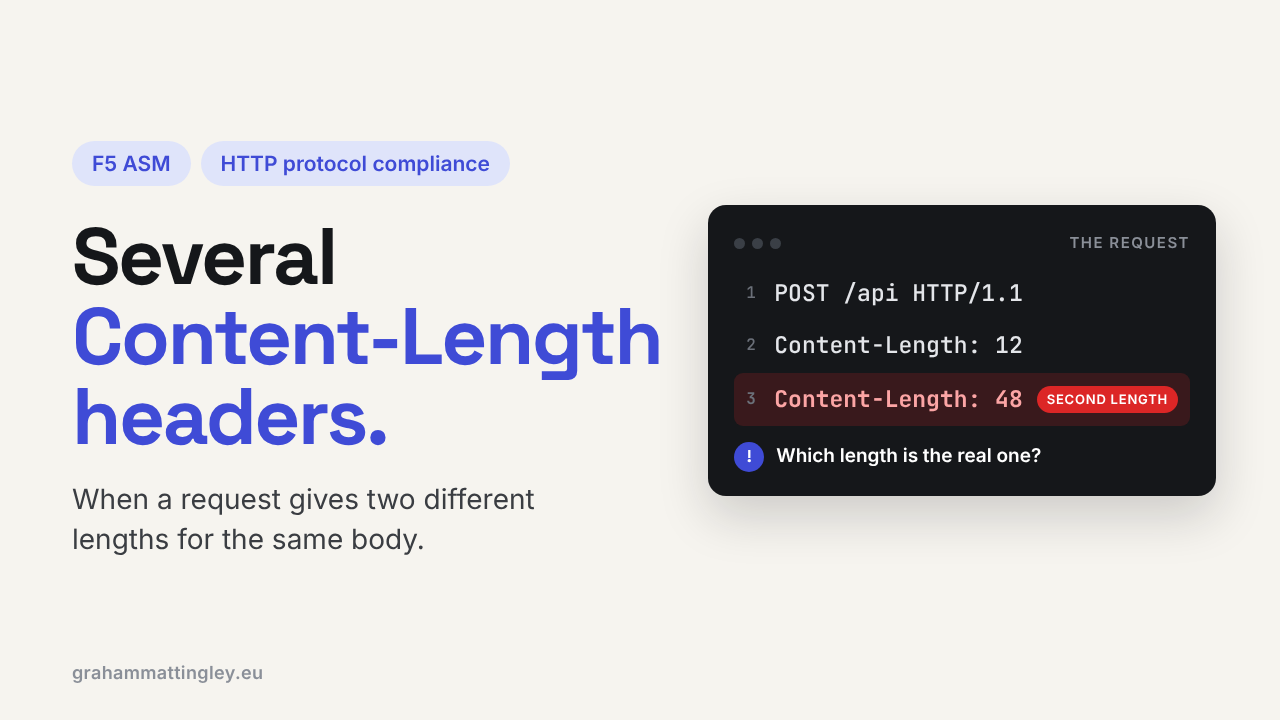
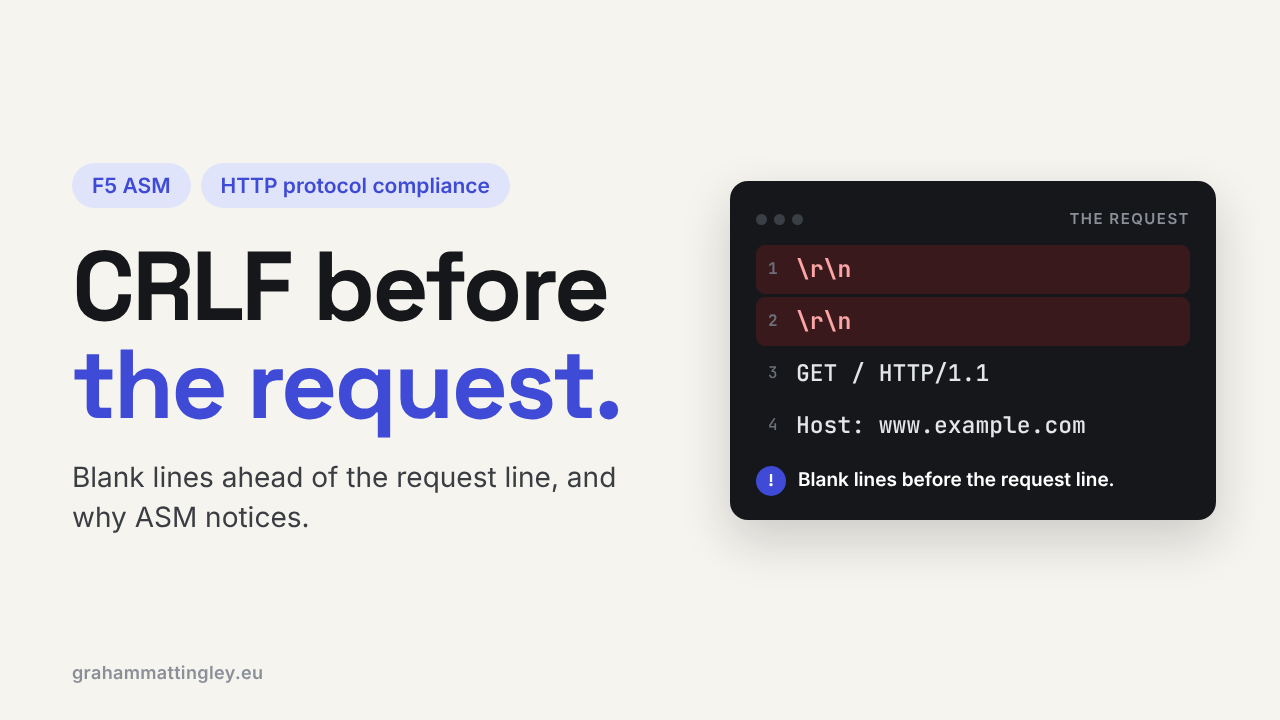
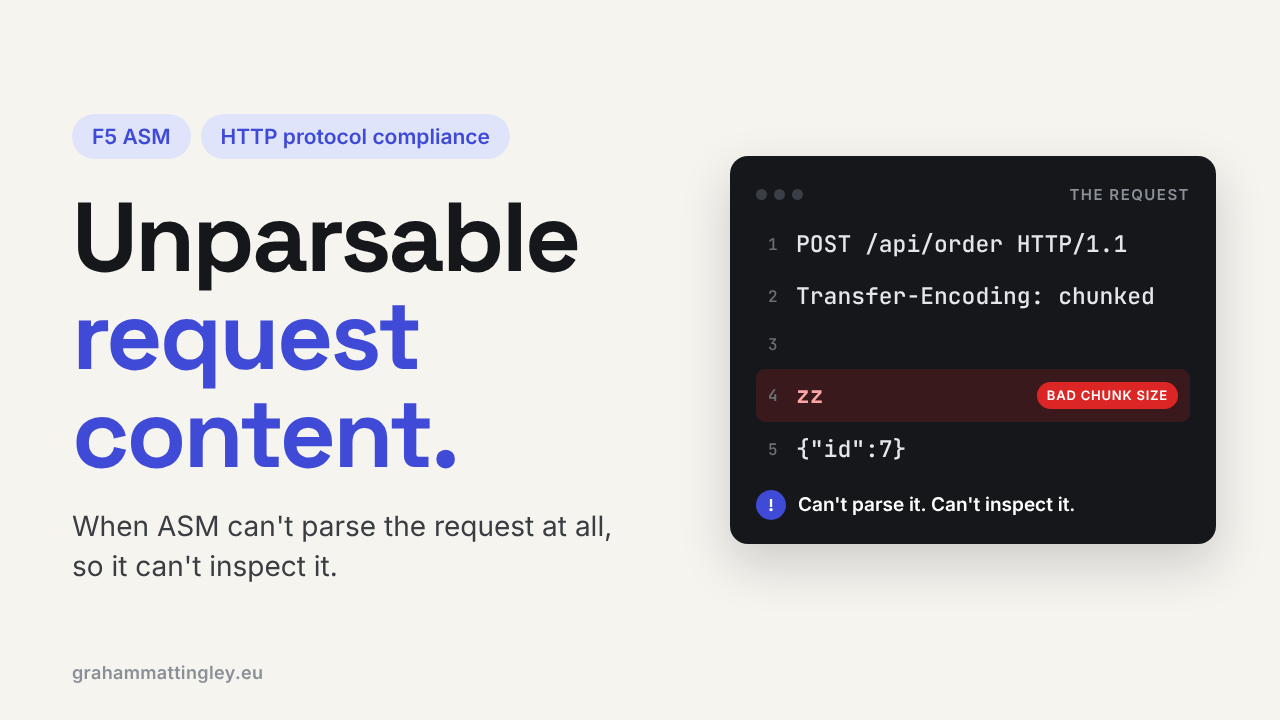
HTTP compliance, violation by violation
Every HTTP protocol compliance check explained on a live policy: what it catches, why it fires, and when to turn it on.
Both sides of the wire
I've built the back-end applications that F5 serves. That changes how I can teach this subject.
Over 30 years as a working developer, building real applications for real companies, and still building today. I've taken it as far as it goes: domain-driven design, n-tier architecture, authentication from the ground up through OAuth, SAML and third-party identity, repositories, CI/CD and containers, and now LLM-assisted development. So when a BIG-IP rewrites a header, terminates a session or blocks a parameter, I can show you what happens at both ends of that connection, not just the F5 end. You learn the box and the application behind it, and exactly how they work together.
And I teach you to speak the developer's language. Much of the professional friction in F5 work is between the development, security and delivery teams, each talking their own language with their own agenda. When you can explain the policy in development terms, the friction disappears and the cooperation starts.
There's a better way to think of the F5 than as a hop on the way to the application. It is the outside layer of the application: the delivery, security and access layer that sits above the user interface. Once you start to think of the F5 as integrated into the application, the magic starts.
Architecture
DDD, n-tier, APIs. What the pool members actually are.
Identity
OAuth, SAML, OIDC, third-party auth. What APM is really brokering.
Delivery
Repos, CI/CD, containers. Where the app comes from and how it changes.
Attack surface
OWASP from the code side. Why the signature fires, not just that it does.
Three ways in
Pick the one that matches where you are.
Exam Blueprint Courses
Every F5 module, mapped line-by-line to the official blueprint and taught from real development workflows, OWASP attack patterns and enterprise delivery.
1:1 Coaching
Work directly with me on your exam, your live issue or your design. Structured path or your own agenda. Every session recorded to your account.
Real-World Community
A members-only room of F5 engineers who have deployed, broken and fixed BIG-IP in production. Questions, war stories, study partners.
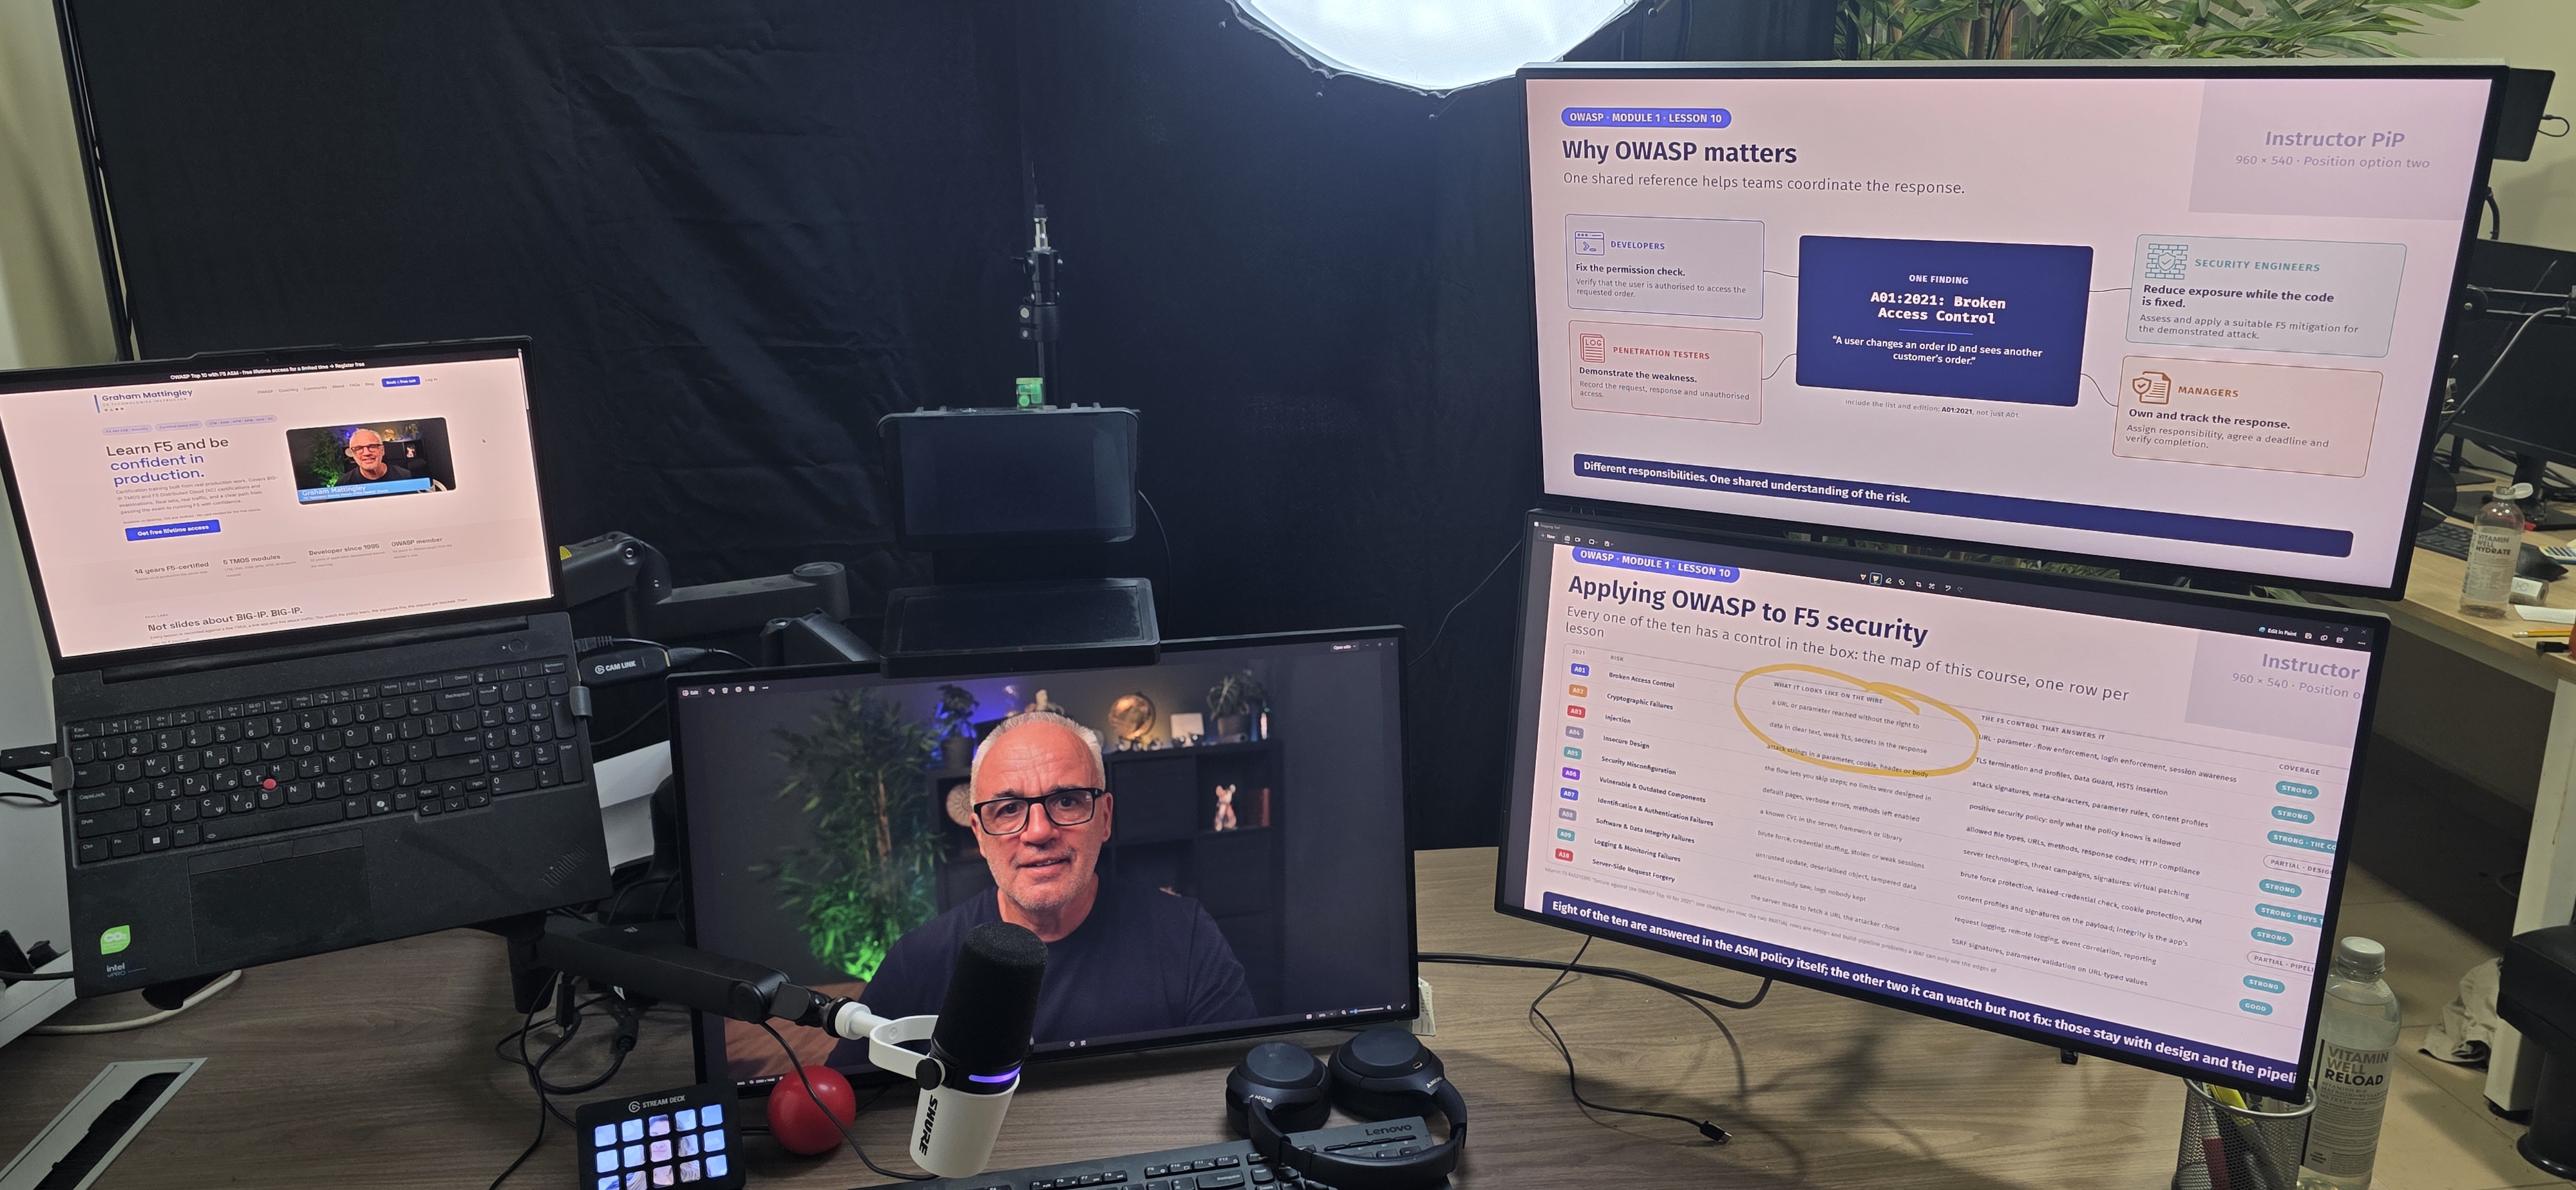
Who's teaching
The F5 skills employers actually look for.
Since 2008 I've worked inside F5's biggest customers: airlines, banks, broadcasters, government, petrochemical, online gambling. Eighteen years of their requirements, their change procedures, their security reviews and their interviews, so I know exactly what they expect from the F5 engineer in front of them.
All of that goes into the courses. Not a blueprint read out loud, but real requirements, real war stories and the hints that tell you how a thing is actually done, and how to explain it to the people who sign it off. The goal is not just a pass. It's being the credible F5 contractor or staff member they hire, and keep.
F5 401 CSE · SecurityLTM · ASM · APM · AFM · DNS · XCOWASP member
More about meFree newsletter
F5 in Practice
No spam. No fluff. One practical insight at a time, written by me from work I've actually done.
Free 20-minute call
Talk through anything F5
Training, a stuck issue, a design review. I'll do my best to sort it in 20 minutes. Slots on Thursdays and Fridays.
Book a callWho is this F5 training for?
Do I need experience with F5 to start?
What makes this different from other F5 courses?
Which modules and exams are covered?
What if I don't pass?
How does 1:1 coaching work?
Is there a community I can join?
How is the training delivered?
How much time do I need to commit?
Start with the free OWASP Top 10 course.
Lifetime access for a limited time. See how the training works before you spend a cent.
Get free lifetime access“
Graham took me through the 201, then the 301a and 301b. He teaches on a real BIG-IP and explains why things work, not just what to click. I passed all three in seven months.
Nikos [surname]
[Job title], [Company] · Passed all 3 in 7 months